Filtering IP Network Traces using Wireshark-Like Expressions
You can filter syslog and debug recording messages for IP network traces, by configuring the 'Filter Type' parameter to IP Trace in the Logging Filters table.
IP traces record any IP stream, according to destination and/or source IP address, or port and Layer-4 protocol (UDP, TCP or any other IP type as defined by http://www.iana.com). Network traces are typically used to record HTTP.
IP Trace is designed exclusively for capturing non-media traffic such as SIP and Syslog. DO NOT use it for media traffic (RTP/RTCP). Restricting captures to non-media traffic prevents device CPU overload during medium-to-high traffic conditions.
If you need to capture media traffic, change the 'Filter Type' parameter to another option (such as Any) instead of IP Trace.
Mediant CE deployed on Azure:
As mentioned previously, IP traces are not intended for capturing media traffic. When the 'Filter Type' parameter is IP Trace, the device handles IP traces based on the configuration of the 'Value' parameter:
| ● | Value is empty (i.e., all): Excludes all UDP packets (i.e., no media is captured). |
| ● | Value is udp: Records UDP ports 0 to 5999 only. Media is not captured because it typically uses ports 6000 and above. |
| ● | Value is udp with a single port: Captures media only for that specific port. |
| ● | Value is udp with a port range: Captures traffic only up to port 5999. Any ports within the range that are 6000 or above are excluded. Media is not captured because it typically uses ports 6000 and above. |
When the IP Trace option is selected, only the ‘Value’ parameter is applicable in the Logging Filters table. This parameter configures Wireshark-like filtering expressions for your IP trace. The following Wireshark-like expressions are supported:
Supported Wireshark-like Expressions for 'Value' Parameter
|
Expression |
Description |
|---|---|
|
and, &&, ==, <, > |
Comparison operators used between expressions. |
|
ip.addr |
Defines IPv4 addresses (up to two) to capture. |
|
ip.dst |
Defines the destination IPv4 address to capture. |
|
ip.proto |
Defines the IP protocol type (PDU) entered as an enumeration value (e.g., 1 is ICMP, 6 is TCP, and 17 is UDP) to capture. |
|
ip.src |
Defines the source IPv4 address to capture. |
|
ipv6 |
Captures all IPv6 packets (source and destination). |
|
ipv6.addr |
Defines IPv6 addresses (up to two) to capture. |
|
ipv6.dst |
Defines the destination IPv6 address to capture. |
|
ipv6.src |
Defines the source IPv6 address to capture. |
|
udp, tcp, icmp, sip, ldap, http, https |
Defines single expressions of the protocol type to capture. |
|
udp.dstport, tcp.dstport |
Defines the transport layer of the destination port to capture. |
|
udp.port, tcp.port |
Defines the transport layer to capture. |
|
udp.srcport, tcp.srcport |
Defines the transport layer of the source port to capture. |
The following are examples of configured expressions for the 'Value' parameter:
| ■ | udp && ip.addr==10.8.6.55 |
| ■ | ip.src==10.8.6.55 && udp.port>=5000 and udp.port<6000 |
| ■ | ip.dst==10.8.0.1/16 |
| ■ | ip.addr==10.8.6.40 |
| ■ | ipv6.addr==2001:0db8:85a3:0000:0000:8a2e:0370:7334 |
| ■ | ipv6.src==2001:db8:abcd:0012::0/64 |
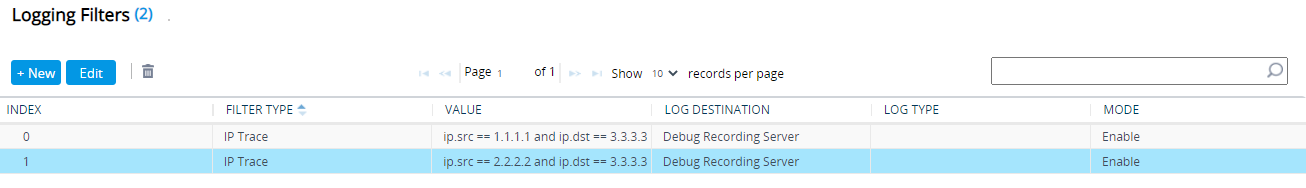
For conditions requiring the "or" / "||" expression, add multiple rows in the Logging Filters table. For example, the Wireshark condition "ip.src == 1.1.1.1 or ip.src == 2.2.2.2" and "ip.dst == 3.3.3.3" can be done by adding two rows in the table, where the 'Value' parameter of each row has the following value:
| ■ | Index #0: 'Value' parameter is configured to "ip.src == 1.1.1.1 and ip.dst == 3.3.3.3" (without apostrophes) |
| ■ | Index #1: 'Value' parameter is configured to "ip.src == 2.2.2.2 and ip.dst == 3.3.3.3" (without apostrophes) |
| ● | If you leave the 'Value' parameter empty, the device records all IP traffic types. |
| ● | You can't configure the 'Value' parameter with both IPv4 and IPv6 addresses. |
| ● | You can't configure the 'Value' parameter with "ip.addr" or "udp/tcp.port" together with "ip.src/dst" or "udp/tcp.srcport/dstport". For example, the following is invalid: |
ip.addr==1.1.1.1 and ip.src==2.2.2.2
| ● | You can't configure the 'Value' parameter with "ipv6.addr" or "udp/tcp.port" together with "ipv6.src/dst" or "udp/tcp.srcport/dstport". For example, the following is invalid: |
ipv6.addr==2001:0db8:85a3:0000:0000:8a2e:0370:7334 and ipv6.src==2001:db8:abcd:0012::0/64